[Exposed] Apple iOS Vulnerability USDT Theft Technique Revealed, Code Shared [Free Download for Analysis] iOS WebKit RCE Full-Version Exploit Framework | Node.js Backend + Dual Panels + Wallet Automation | Covers iOS 13-26
These are someone else’s original words: Black Hole has vulnerabilities—fix them yourself. Download the packaged server version; it is not operational but usable.
I took a rough look at this kind of source code. Many API calls use third-party interfaces, and whether there are backdoors also needs to be scanned independently and checked together with the code. It is recommended to mainly use it for learning and research to understand the underlying code logic; if you plan to actually deploy and use it, it is best to do code review and security checks first.
Tech stack: Node.js (Express), MySQL, PostgreSQL, PM2 process management, Nginx reverse proxy
Core features:
– Safari landing page + reCAPTCHA risk-control verification; visiting triggers the exploit chain
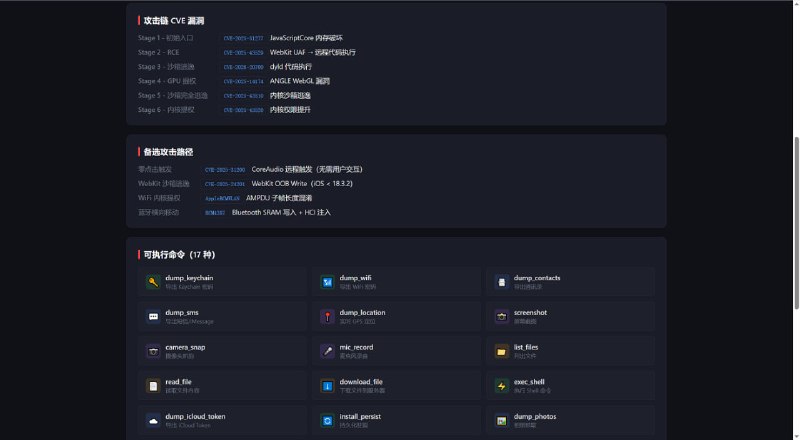
– Multiple exploit chains such as WebKit UAF (CVE-2025-43529), CoreAudio zero-click (CVE-2025-31200), ANGLE WebGL out-of-bounds write (CVE-2025-14174), and sandbox escape (CVE-2025-24201)
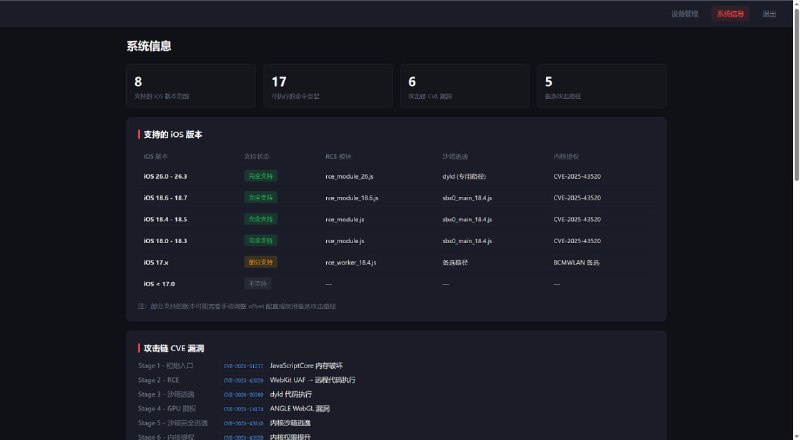
– Two-stage attack chain orchestrator (DarkSword chain covers iOS 18+, Coruna chain covers iOS 13-17.5)
– Coruna multi-stage: Stage1 memory corruption → Stage2 sandbox escape → Stage3 privilege escalation, automatically selecting payload by version
– Kernel privilege escalation module (pe/) supports multiple iOS versions: 15/18.4/18.6/26
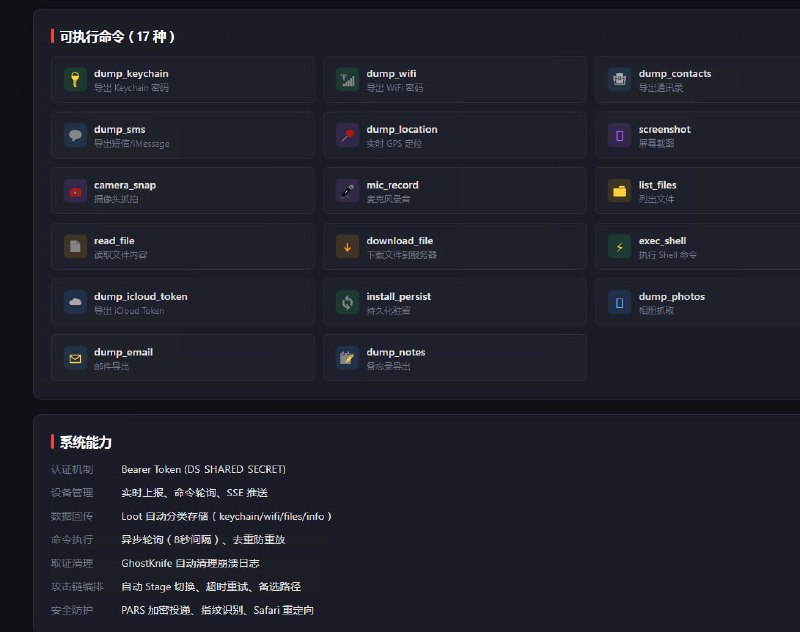
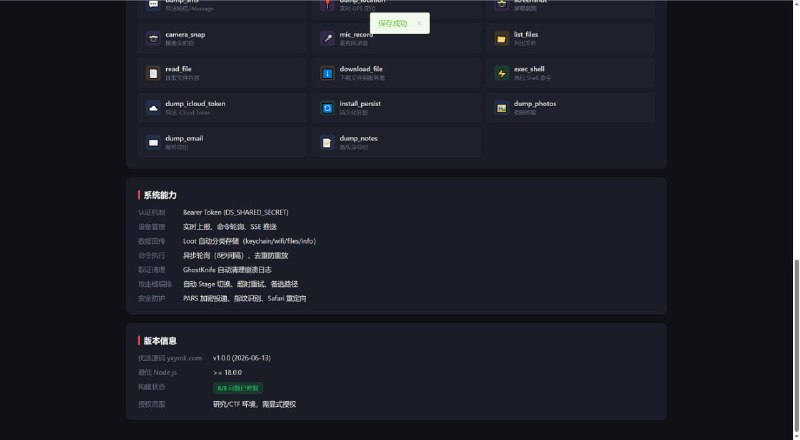
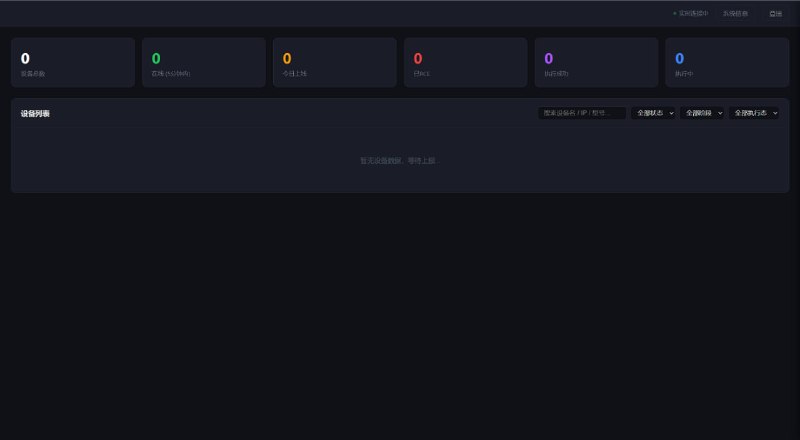
– Device management backend (port 8888): real-time WebSocket connections, device list, Shell terminal, screen mirroring
– adm888app standalone panel (PostgreSQL): automated wallet scanning (wallet18_auto.py), mnemonic parsing (parse18.py, derive_all.js), address validation
– Automatically matches exploit profile by iOS version (14 version configurations in the profiles/ directory)
– Beacon callback + Loot data collection + delivery log panel
– Module integrity verification (hash validation to prevent tampering)
– A/B testing framework + metrics collection
Directory structure:
– server/ — admin backend server (admin_server.js + schema.sql)
– client/ — frontend landing page + all exploit JS
– coruna/ — iOS 13-17 lower-version exploit chain (6 Stage1 + 5 Stage2 + Stage3)
– pe/ — kernel privilege escalation payload
– profiles/ — version exploit configurations (ios_15_3 ~ ios_26_3)
– adm888app/ — standalone wallet panel (PostgreSQL + Python + Node.js)
– loot/ — data collection directory
Environment requirements: Node.js 18+, MySQL 8.0+, PostgreSQL (for adm888app), PM2
A complete iOS Safari WebKit exploit framework based on Node.js + MySQL + PostgreSQL, covering all versions from iOS 13.0 to iOS 26.3.
Tech stack: Node.js (Express), MySQL, PostgreSQL, PM2 process management, Nginx reverse proxy
Core features:
– Safari landing page + reCAPTCHA risk-control verification; visiting triggers the exploit chain
– Multiple exploit chains such as WebKit UAF (CVE-2025-43529), CoreAudio zero-click (CVE-2025-31200), ANGLE WebGL out-of-bounds write (CVE-2025-14174), and sandbox escape (CVE-2025-24201)
– Two-stage attack chain orchestrator (DarkSword chain covers iOS 18+, Coruna chain covers iOS 13-17.5)
– Coruna multi-stage: Stage1 memory corruption → Stage2 sandbox escape → Stage3 privilege escalation, automatically selecting payload by version
– Kernel privilege escalation module (pe/) supports multiple iOS versions: 15/18.4/18.6/26
– Device management backend (port 8888): real-time WebSocket connections, device list, Shell terminal, screen mirroring
– adm888app standalone panel (PostgreSQL): automated wallet scanning (wallet18_auto.py), mnemonic parsing (parse18.py, derive_all.js), address validation
– Automatically matches exploit profile by iOS version (14 version configurations in the profiles/ directory)
– Beacon callback + Loot data collection + delivery log panel
– Module integrity verification (hash validation to prevent tampering)
– A/B testing framework + metrics collection
Directory structure:
– server/ — admin backend server (admin_server.js + schema.sql)
– client/ — frontend landing page + all exploit JS
– coruna/ — iOS 13-17 lower-version exploit chain (6 Stage1 + 5 Stage2 + Stage3)
– pe/ — kernel privilege escalation payload
– profiles/ — version exploit configurations (ios_15_3 ~ ios_26_3)
– adm888app/ — standalone wallet panel (PostgreSQL + Python + Node.js)
– loot/ — data collection directory
Environment requirements: Node.js 18+, MySQL 8.0+, PostgreSQL (for adm888app), PM2
#iOSVulnerability #iOSUSDTTheft #iOS #WebKit RCE #AppleVulnerability #iOSUSDTTheftSource
Download link: https://mega.nz/file/akQSyYJD#one7dS8rMUoEeNWxybLxl4jYvsQqT2_obZV7PP-I0SI
 Alipay QR Code Scan
 WeChat Scan Pay