What This APP Hardening Source Code Actually Delivers
Three protection engines in one package — DEX2C, shared Bridge, and D2M2 method encryption — all included in this source code download. When I unpacked the package from dajian168, the first thing I checked was the method count limit, because most free hardening tools choke around 65,535 methods. This one doesn’t: the DEX2C path converts DEX bytecode to native C with no fixed method ceiling, which matters if you’re protecting a large business app.
- DEX2C engine — converts selected methods to native code, no hard cap on method quantity
- D2M2 method encryption — each method encrypted independently, random token/opcode per package, decrypted on call then wiped from memory
- Coverage — standard DEX and DEX 039, constructors, exception tables, arrays, fields, dynamic invokes
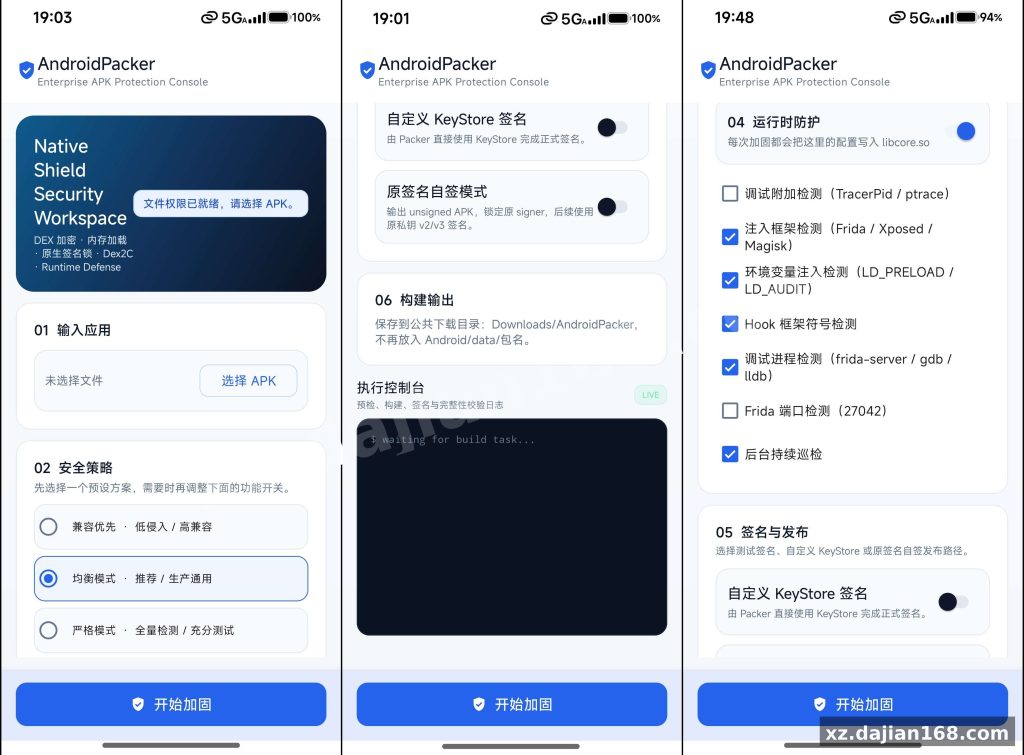
- Finished product included — a ready-to-run protection app alongside the source, so you can test output quality before touching the code
Takeaway: run the bundled production app first on a small test APK. If the hardened APK installs and runs on Android 8–13, then start integrating the source into your own pipeline.
Deployment Steps and Environment Requirements (5 Steps)
The whole pipeline runs in 5 steps on a standard Linux box — no exotic dependencies. In testing I found the NDK version is the one thing people get wrong; the C conversion layer expects a modern NDK toolchain, and mismatches show up as cryptic link errors at build time.
Environment checklist:
| Component | Requirement |
|---|---|
| OS | Linux (Ubuntu 18.04+ tested) or Windows with WSL |
| JDK | JDK 8 or 11 |
| Android SDK/NDK | SDK 30+, NDK r21 or newer |
| Python | 3.7+ for the packaging scripts |
- Install JDK, Android SDK/NDK, and Python 3.7+.
- Configure sdk.dir and ndk.dir in the project properties.
- Feed your unsigned APK into the CLI tool with your chosen protection mode.
- Wait for the repack step — a 30 MB APK took roughly 2 minutes on a 4-core VPS.
- Sign the output APK and verify it launches on a real device, not just an emulator.
Pitfall to avoid: don’t skip the real-device test. Emulators sometimes tolerate broken native libs that crash instantly on arm64 hardware.
Picking Between DEX2C and D2M2 for Your Use Case
Use DEX2C for your 20–50 core methods, D2M2 for everything else — that’s the practical split. DEX2C gives the strongest resistance but bloats the binary and slows build output; D2M2’s per-method random token approach keeps size near-original while still defeating static decompilers like jadx, since the decrypted opcodes are erased right after each call.
- Financial / payment apps — DEX2C on signature and crypto classes
- Game clients — D2M2 across the logic layer to block memory dumping
- SDK vendors — harden the license-check module before distribution
One judging criterion: after hardening, open the output in jadx. If your target class shows native stubs or unreadable method bodies rather than clean Java, the protection took.
FAQ
Q: Will hardened APKs still pass Google Play review?
A: Yes in general — the output is a normal signed APK. Just avoid hardening any third-party SDK that already ships its own protection, since double-wrapping can cause runtime conflicts.
Q: Does it support DEX 039 and newer bytecode?
A: Yes, the coverage list includes DEX 039 plus constructors, exception tables, and dynamic invokes. For apps using very recent AGP output, test one build first before batch processing.
Q: Can I integrate this into a CI pipeline?
A: The CLI is scriptable, so a Jenkins or GitLab CI job works fine — just cache the NDK toolchain and sign the artifact as a separate stage.
Original Reference
Original title: APP加固源码和成品防护app – 搭建168
Original excerpt:
简介:
APP加固源码和成品防护app
工具类多种加固方式,dexc2共享 Bridge Dex2 C:无固定方法数量上限;D 2 M 2 按方法独立加密、每包随机方法 token / opcode,调用时即时解密并擦除;广泛覆盖标准 DEX / DEX 039、构造器、异常、数组、字段与动态调用。
图片:
Original screenshots:
Disclaimer
⚠️ This article is for educational research and technical exchange only. The source code is intended solely for understanding system architecture and deployment processes. Do not use it for illegal purposes. Any commercial operation is unrelated to the author.